Critical Vulnerability Found in x402 SDK, Exposing AI Agents to Malicious API Risks
A critical flaw in the x402 SDK could expose AI agents to malicious interfaces when calling external APIs, though affected versions and attack paths remain undisclosed.
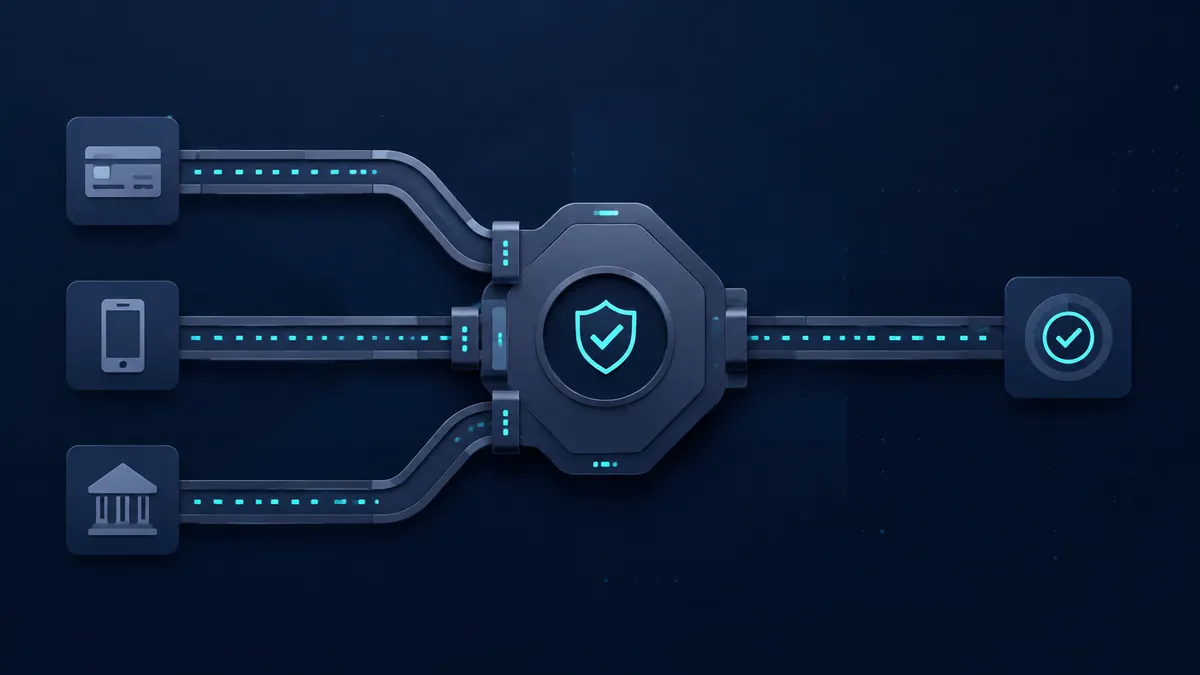
According to a report by SecNews.gr, a critical vulnerability exists in the software development kit (SDK) of x402, a machine payment protocol built on HTTP 402, which could expose AI agents to malicious interfaces when calling external APIs. The report did not disclose the affected SDK versions, vulnerability identifiers, or specific attack paths.
x402 is designed to enable AI agents to complete machine-to-machine payments within automated workflows, and the SDK serves as the primary entry point for developers integrating the protocol. If agents lack verification of interface origins and returned content when calling third-party APIs, the attack surface could extend from the payment layer to the agent's call chain.
As of the time of reporting, there were no records of the vulnerability being exploited in practice, nor any official patched versions or patch notes. For teams relying on x402 to build agent payments, SDK interface validation and caller identity verification are the areas that need to be checked at present.
Source: https://news.google.com/rss/articles/CBMiggFBVV95cUxONU5TTU1xOG4zU3RQS2xCYlRWaUlDczhvemQtMjg2bkZHNGRVRGpGWXZ6djkxYWxZZVBEMUpnSFJpV2N0TFc0VkRpQTJkcWlfemlkTHBxMGZ0SWRybkhOdjgxNHVBVEFIY0VOcW14MWVfWVJOc0txd3ZYa1pVMnlDdkdB?oc=5
Provenance & status
- Byline
- OceanAlt Editorial
- First published
- 2026-10-24
- Last updated
- 2026-10-24
- Content type
- Newsflash
- Source material
- View original ↗
Related reading
Paste a payee address before you pay and see whether it's on a sanctions list, through a mixer, or tagged for fraud.
This judgement can sit inside your own product
One line of code; it touches neither your CSS nor your JS. The same pre-settlement judgement can appear in your articles, on your wallet's confirmation screen, or as an endpoint your agent calls before it pays.